

Fix Moment.js vulnerabilities without rewriting your date code
Moment is in maintenance mode, and upstream fixes go to current releases. Endless Lifecycle Support delivers security-patched builds of covered moment and moment-timezone versions through npm, backed by a contractual SLA.
Moment 2.0.0, 2.10.6 and 2.24.0
plus moment-timezone 0.4.1
Jump to:

Talk to Us
Ask about coverage, SLAs, pricing, or anything else.


Moment.js versions covered by ELS
 Covered package version |
 Superseded by a newer upstream release |
 ELS coverage |
|---|---|---|
| moment 2.0.0 | July 2013 |
 Covered by ELS |
| moment 2.10.6 | January 2016 |
Covered by ELS
|
| moment 2.24.0 | May 2020 |
Covered by ELS
|
| moment-timezone 0.4.1 | December 2015 |
Covered by ELS
|
Moment has no published EOL calendar, so the dates show when each release was superseded upstream.
Pinned to something else?
Tell us what you run and we will look at coverage options.
Request Coverage
What You Get with ELS

Security fixes for the versions you already run
TuxCare backports applicable security fixes to covered moment and moment-timezone releases, including releases upstream no longer patches, and keeps tracking new disclosures.
On day 1
Every fix TuxCare has already shipped for your covered release is waiting the moment you point npm at the ELS registry.

Patch without reworking your application
ELS provides a security-patched package built to preserve the version and behavior your project expects.
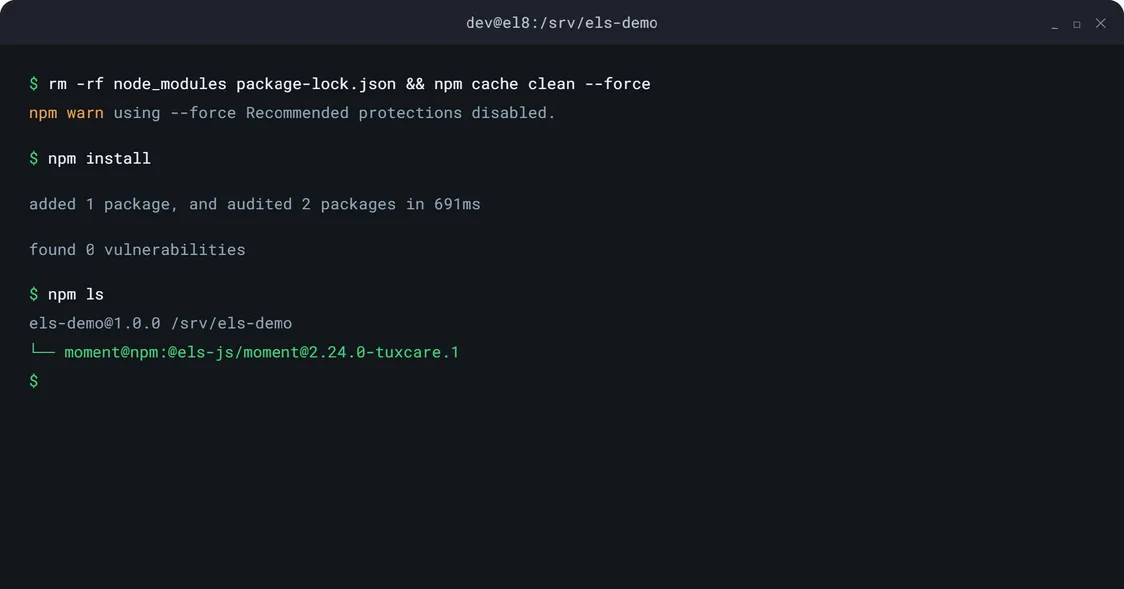
Update the package reference, install from the TuxCare npm registry, and keep your application code, Docker builds and CI/CD process as they are.

A documented remediation path
Patch Delivery Under SLA
Support older dependencies with vendor-maintained packages and a contractual SLA your security and compliance teams can review.
Enterprise Support Guarantees
Commercial terms and contractual protections that volunteer maintenance was never meant to provide.
Patch covered Moment releases in your normal npm workflow
Three steps, no new tooling, and nothing that touches your application code.
Ask us about your Moment.js version
Tell us which releases sit in your dependency tree and we will walk through coverage options.
Ask Us a Question
Three step install
-
Configure the TuxCare registry. Add the registry lines and your token to
.npmrc.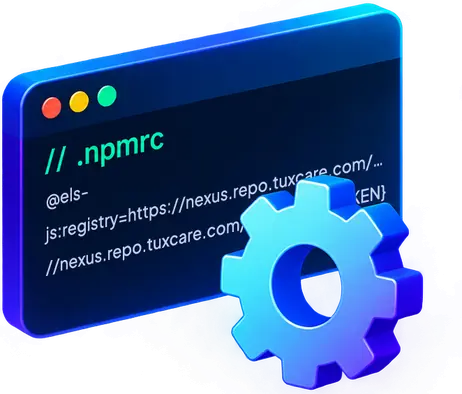
-
Point the dependency at the patched package. Update the package reference in
package.jsondirectly, or use the TuxCare Patcher.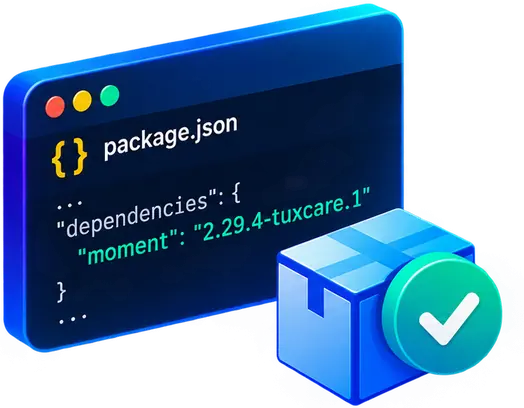
-
Clear and reinstall. Remove
node_modulesand the lockfile, clear the npm cache, then runnpm install. Docker and CI/CD builds resolve it the same way.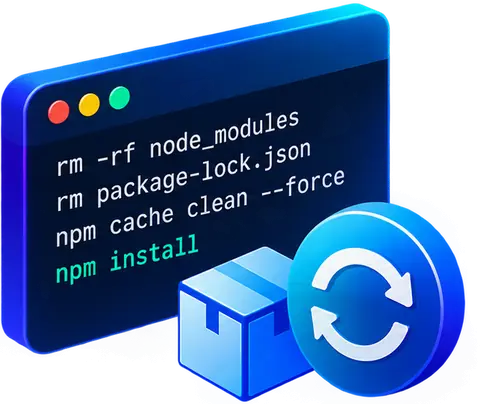
How Teams Use ELS

Fix the flaw, not just the alert
⚠️ The bind:
An old moment release keeps showing up in scan results, and the fix upstream only exists in a version you cannot reach yet.
🔄 The turn:
ELS delivers the applicable fix on your covered release, so the vulnerability is actually remediated rather than deferred.

Migrate off Moment on your schedule
⚠️ The bind:
Replacing Moment can affect parsing behavior, formatting tokens, locales, time zone handling, integrations and tests.
🔄 The turn:
ELS keeps covered versions patched while your team inventories usage, picks an alternative and migrates deliberately.

Answer the questionnaire properly
⚠️ The bind:
Security reviews keep landing on the same legacy dependency, and there is no date to put next to it.
🔄 The turn:
ELS supplies a named vendor, an SLA and a remediation record, which is what the reviewer is actually asking for.
Why TuxCare?
 420,000+
Patches Delivered
From the Team That Extends Open-Source Lifecycles
Keeping software patched after upstream moves on is what TuxCare does, across the Linux kernel, language runtimes and libraries such as Moment.js.
 14,000+
Vulnerabilities Fixed
Founding platinum sponsor of the AlmaLinux OS Foundation and member of the Open Source Security Foundation (OpenSSF).
TuxCare invests in the open-source ecosystem it secures, from Moment.js to Linux, and beyond.
Learn more → 70,000+
Packages Curated
 2,700+
Enterprise Clients

Related Insights
Top 5 Patch Management Tools in 2026: Full Review
Key Takeaways Patch management tools often look alike on a feature list, but they…

CVE-2026-98276 Was Fixed Upstream. Then a Server Crashed 12 Times.
KernelCare Rebootless Patches for CVE-2026-98276 Are Out for EL 8 and 9 TuxCare has…
The SSH Authentication Bypass That Lived Between OpenSSH and musl (CVE-2026-123158)
Key Takeaways A password of 257 to 1024 bytes logs in to any key-only…
Patch the version you have. Migrate when it suits you.
Covered moment and moment-timezone releases keep getting security fixes through the npm workflow you already use.
Ask Us a Question
Frequently Asked Questions
Yes, in maintenance mode. Moment.js is an OpenJS Foundation At-Large project maintained by volunteers. The August 2026 Moment.js project status update says the maintainers expect further 2.x maintenance releases, will address critical security concerns, and no longer categorically rule out a maintenance-oriented Moment 3.0. Moment.js 2.31.0 was published on 15 September 2026. Security fixes land on current releases rather than on the older versions many applications pin.
Moment.js 2.0.0 and 2.10.6 are affected by CVE-2016-4055 and CVE-2017-18214, both regular expression denial of service, and by CVE-2022-24785, a path traversal in locale switching. Both are also affected by a further ReDoS advisory covering versions below 2.15.2, which carries no CVE identifier and is tracked by Snyk as npm:moment:20161019. Moment.js 2.24.0 is affected by CVE-2022-24785 and by CVE-2022-31129, another ReDoS. Upgrading has not closed the locale path traversal for good. CVE-2026-17495, disclosed on 15 September 2026, affects Moment.js 2.29.2 through 2.30.1 because it bypasses the locale-name guard those versions introduced to fix CVE-2022-24785. Teams that upgraded in 2022 to close CVE-2022-24785 ended up inside the range of its incomplete fix, and the remedy is another upgrade to 2.31.0.
Replace the vulnerable package with a security-patched build of the same version. TuxCare Endless Lifecycle Support publishes maintained Moment.js packages through the TuxCare npm registry. Add the registry to .npmrc, point package.json at the ELS package manually or with the TuxCare Patcher, remove node_modules and the lockfile, clear the npm cache, then run npm install. The packages are drop-in replacements for the upstream releases they match, so the application keeps calling the same Moment.js API.
TuxCare Endless Lifecycle Support covers Moment.js 2.0.0, 2.10.6 and 2.24.0, plus Moment Timezone 0.4.1. Moment Timezone is a separate npm package and is listed separately. Coverage is version specific, so the installed package matches the release line the application already expects. Applications pinned to a different version can contact TuxCare about coverage options.
Yes. Moment.js often arrives through date pickers, charting libraries and other components rather than through a direct import. TuxCare ELS packages resolve from the TuxCare npm registry, and npm overrides in package.json redirect covered instances in the dependency tree to the maintained package. The TuxCare Patcher can detect covered versions and write those overrides. The same packages install in Docker builds and CI/CD pipelines.
Partly. TuxCare Endless Lifecycle Support is designed to support vulnerability-remediation requirements for Moment.js under frameworks including SOC 2, PCI DSS, HIPAA, NIS2, DORA and the EU Cyber Resilience Act. It does not make an application compliant on its own. What it provides is a named vendor, a contractual SLA and a documented remediation path that auditors can review.
Both can be right, and the deciding factor is how deeply Moment.js is used in the application. The August 2026 project status update walks back the 2020 advice against new projects and reports that weekly downloads have more than tripled, so the case for ripping Moment.js out is weaker than it was. For a mature application with years of parsing, formatting, locale and time zone logic built on the Moment.js API, TuxCare ELS keeps covered releases patched while migration happens on a planned schedule, or while the application stays on Moment.js by choice.