Tech Support
 Documentation
 Login
 Contact Us



Go straight to an AI summary of this blog post instead 


Key Takeaways
- Cloud security standards fall into five enforcement types, from certifications and attestations to regulations, contracts, and control frameworks.
- ISO/IEC 27017 got its first full rebuild since 2015, FedRAMP rewrote its rulebook, and CSA shipped CCM v4.1.
- Patching shows up in nearly every standard here, but only a handful put a hard deadline on it.
- Most audit pain builds up between assessments, while patch backlogs grow and configurations drift.
So much of what a modern business runs on now lives on infrastructure it doesn’t own, and that shift changed who’s accountable for security. It also multiplied the rulebooks a security team has to satisfy at once. Cloud security standards are those rulebooks, written down.
This article covers what cloud security standards are, why the type of standard matters, and which 14 matter most for cloud compliance programs in 2026.
What Is Cloud Security?
Cloud security is the set of controls that protect workloads, identities, and data in cloud environments, which usually means servers someone else runs. It spans configuration, encryption, access management, patching, and monitoring across IaaS, PaaS, and SaaS. In IaaS, the provider looks after the physical hosts and the hypervisor, and you own nearly everything from the guest OS up. In SaaS, the provider runs most of the stack, so your job narrows to identity, tenant configuration, and what people do with the data. PaaS sits between the two.
What Are Cloud Security Standards?
Cloud security standards are published requirements that define what “secure enough” looks like in the cloud, and they give auditors and regulators something concrete to test against. Some come with a real certificate that expires and gets renewed. Some produce an attestation report instead of a pass or fail badge. Some are law, with fines behind them. Others are voluntary guidance that organizations adopt because a customer, an auditor, or their own risk assessment points them there.
That last category overlaps with what people usually call cloud security frameworks: NIST CSF, CSA’s Cloud Controls Matrix, and similar reference sets built for guidance rather than certification. The overlap is real, and it runs both ways. Plenty of “standards” roundups include NIST CSF and CCM, even though both describe themselves as voluntary.
This guide uses “standard” as the umbrella term for security requirements in cloud computing broadly, and sorts each entry by how it actually gets enforced (certification, attestation, regulation, contractual requirement, or control framework) instead of drawing a hard line between “standards” and “frameworks.”
Why Cloud Security Standards Matter
Two reasons: they gate revenue, and they gate risk. Plenty of enterprise buyers won’t sign until a SOC 2 report or an ISO certificate is on file. And regulators can come after you for GDPR or HIPAA violations whether you hold a certificate or not.
For compliance-driven organizations, standards do something more concrete than signal good intent. They translate “we take security seriously” into control language a regulator, an auditor, or a procurement team can actually check.
Reality Check: Passing an audit doesn’t prove your controls work every day in between. ISO 27001 surveillance audits typically come around once a year, and a SOC 2 Type II observation window can run most of a year on its own. Between those checkpoints, patch backlogs grow, configurations drift, and new services get spun up outside the scope the last audit covered. Without continuous monitoring, a lot of that won’t surface until the next assessment does. Our list of current cloud security threats covers what tends to pile up in that gap.
Top 14 Cloud Security Standards
What kind of standard you’re looking at determines what you actually have to do about it. Mixing up the five types is how teams end up promising a customer an “ISO 27017 certificate” that doesn’t exist as a standalone thing, or telling an auditor they’re “NIST CSF certified” when CSF has no certification track at all.
| Standard | Governing body | Type | Who needs it |
| ISO/IEC 27017:2026 | ISO/IEC | Control framework (assessed within an ISO/IEC 27001 audit) | Cloud providers and customers |
| SOC 2 | AICPA | Attestation | SaaS and service organizations selling to US enterprises |
| GDPR | EU / national DPAs | Regulation | Anyone processing personal data of people in the EU |
| HIPAA | US HHS Office for Civil Rights | Regulation | Covered entities and business associates |
| PCI DSS v4.0.1 | PCI Security Standards Council | Contractual standard | Anyone storing, processing, or transmitting card data |
| ISO/IEC 27001:2022 | ISO/IEC | Certification | Organizations needing a certified ISMS |
| ISO/IEC 27018:2025 | ISO/IEC | Control framework (assessed within an ISO/IEC 27001 audit) | Public cloud providers acting as PII processors |
| CSA STAR / CCM v4.1 | Cloud Security Alliance | Control framework, with STAR attestation or certification | Providers publishing assurance to the STAR Registry |
| NIST SP 800-53 Rel. 5.2.0 | NIST | Control framework (control catalog) | US federal systems and anyone inheriting FedRAMP controls |
| NIST CSF 2.0 | NIST | Control framework (voluntary) | Any organization structuring a security program |
| FedRAMP | FedRAMP PMO / GSA | Certification | Cloud services sold to US federal agencies |
| NIS2 Directive | EU / national authorities | Directive (law via national transposition) | Essential and important entities across 18 EU sectors |
| DORA | EU / European Supervisory Authorities | Regulation | EU financial entities, with oversight of critical ICT providers |
| CIS Benchmarks & Controls v8.1 | Center for Internet Security | Control framework (safeguards and configuration baselines) | Any team hardening cloud infrastructure |
1. ISO/IEC 27017 (2026 Edition)
ISO and IEC jointly maintain this one through their joint technical committee for information security, and the 2026 edition is a real rebuild, not a light refresh. Published in July 2026, it fully replaces the 2015 original and moves the standard onto the ISO/IEC 27002:2022 control structure, in place of the 2013 structure it was built on.
The 2015 edition carried seven extra cloud controls with CLD numbers, covering things like virtual machine hardening and returning customer assets when a contract ends. The 2026 edition trims the cloud-specific additions to four: the baseline shared-responsibility split between provider and customer, an agreement on the roles and responsibilities of any cloud service partner involved, such as a broker or auditor sitting in the provider’s supply chain, segregation in virtual computing environments, and detection and prevention of unauthorized cloud use.
Most of the remaining cloud guidance now sits as cloud-specific notes layered onto the relevant ISO/IEC 27002:2022 controls themselves.
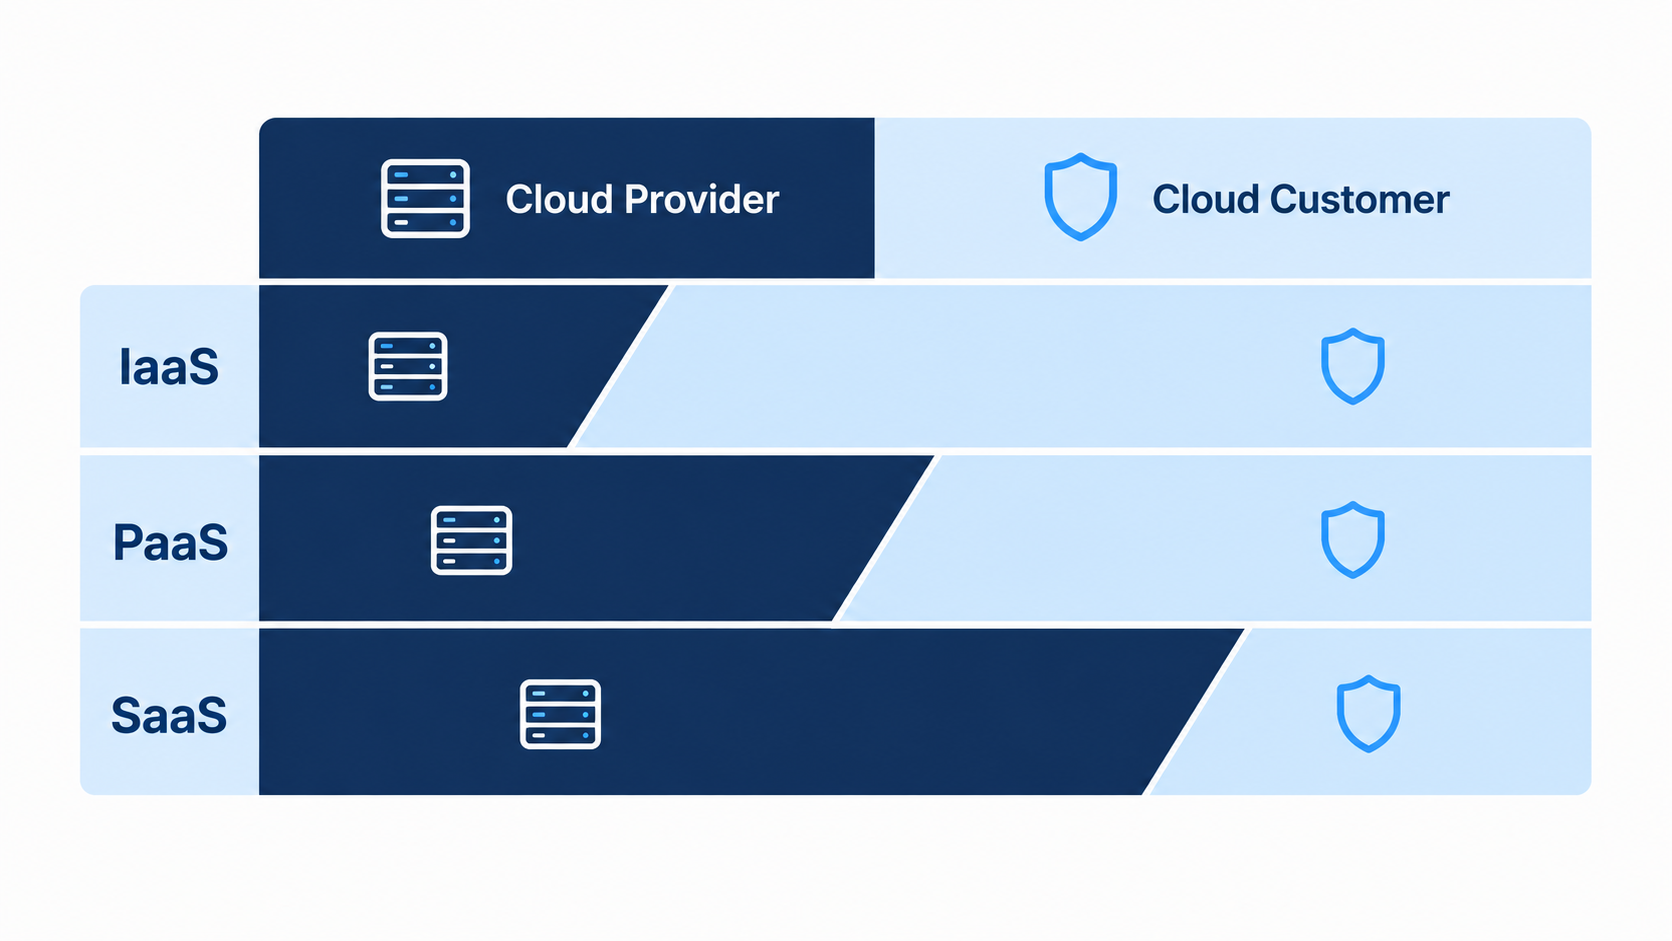
As before, there’s no standalone certificate for this one. It gets audited as part of an ISO/IEC 27001 certification with cloud services in scope. If your compliance documentation still cites the old seven-control set by its CLD numbers, it’s referencing a superseded structure, and an assessor working from the 2026 edition may well flag it.
It’s most useful for cloud providers proving control maturity to enterprise buyers, and for customers who want the division of duties in a cloud relationship written into something more concrete than a sales conversation.
2. SOC 2
SOC 2 comes from the AICPA, and it works differently from most items on this list. A licensed CPA firm examines your controls and issues an opinion report. There’s no official “SOC 2 certified” badge, whatever a vendor’s homepage might imply.
The examination runs against the 2017 Trust Services Criteria, with revised points of focus the AICPA issued in 2022 to keep the guidance current against newer technologies and threats. The underlying criteria themselves haven’t changed since 2017. There are five categories: security, availability, processing integrity, confidentiality, and privacy. Security is required in every SOC 2 report, and you add the rest based on what you’ve committed to customers.
Type I reports describe control design at a single point in time. Type II reports describe operating effectiveness over a period, commonly somewhere between three and twelve months, and that’s the one enterprise buyers usually ask for. Our guide to meeting and maintaining SOC 2 compliance covers the tension between uptime commitments and patching windows.
3. GDPR
GDPR, formally Regulation (EU) 2016/679, applies to organizations established in the EU, and to organizations outside the EU that offer goods or services to, or monitor the behavior of, people in the EU. For cloud specifically, the controller-processor split matters most. You need a Data Processing Agreement, documented safeguards for transfers outside the European Economic Area, and a process that lets the controller notify the supervisory authority without undue delay and, where feasible, within 72 hours of becoming aware of a reportable breach. Processors, for their part, have to tell controllers without undue delay.
Maximum fines run to EUR 20 million or 4% of global annual turnover, whichever is higher.
4. HIPAA
The Health Insurance Portability and Accountability Act (HIPAA) sets the baseline for protecting health information in the US, enforced by the HHS Office for Civil Rights. Like GDPR, it’s law rather than a voluntary framework. It applies to covered entities (healthcare providers, health plans, and healthcare clearinghouses) and to their business associates. A cloud provider that creates, receives, maintains, or transmits electronic protected health information (ePHI) on a covered entity’s behalf is a business associate, even if it never looks at the data.
A Business Associate Agreement spells out each party’s responsibilities and contractually requires the provider to safeguard ePHI. A cloud provider in that role is also directly liable for complying with the applicable HIPAA requirements, and that liability doesn’t depend on the BAA.
The technical requirements live in the Security Rule: access control, audit controls, integrity, transmission security, and risk analysis. A proposed update would scrap the current split between “required” and “addressable” specifications and make encryption, multi-factor authentication, and a documented technology asset inventory mandatory, with only limited exceptions. As of October 2026, that final rule still hasn’t been published. HHS’s regulatory agenda now lists July 2027 as the target, after an earlier May 2026 target came and went.
5. PCI DSS
The PCI Security Standards Council publishes this one, and the current version is v4.0.1. The name says “standard,” but the enforcement is contractual. Your acquiring bank and the card brands do the enforcing, not a government regulator.
The dates that matter here have already passed. Version 4.0 introduced a wave of new requirements, and the 51 that were future-dated became mandatory on March 31, 2025. All of them are live now, with no grace period left to lean on.
PCI DSS also has one of the most explicit patching mandates on this list. Requirement 6.3.3 says patches for critical vulnerabilities go in within one month of release, while every other applicable patch follows a timeframe the entity sets from its own risk ranking. The original v4.0 language briefly stretched that one-month window to cover high-severity patches too. The council reverted it to critical-only in v4.0.1, which is the narrower, current requirement. Requirement 11.3.1 separately calls for internal vulnerability scans at least once every three months and after any significant change.
6. ISO/IEC 27001 (2022 Edition)
Unlike ISO/IEC 27017 and 27018, ISO/IEC 27001 gets you a real, standalone certificate. An accredited certification body audits your information security management system and issues a certificate on a three-year cycle, with annual surveillance audits keeping it honest in between.
The 2022 revision reworked Annex A significantly, consolidating 114 controls into 93 and grouping them into four themes. Eleven brand-new controls came in alongside that restructuring, including threat intelligence, information security for cloud services, and data leakage prevention.
The transition window from the 2013 edition closed on October 31, 2025, and certificates still on the 2013 edition are no longer valid. If your organization missed the transition, expect a fresh initial certification audit rather than a lighter transition audit.
7. ISO/IEC 27018 (2025 Edition)
Maintained by the same ISO/IEC committee as ISO/IEC 27017, this one shares a similar structure. It isn’t independently certifiable. It’s guidance that complements an ISO/IEC 27001-based ISMS, and some certification bodies will assess against it alongside a 27001 audit. It’s now in its third edition, published in August 2025 to replace the 2019 version, with its controls realigned to ISO/IEC 27002:2022 and a new Annex B added.
Where 27017 covers cloud security broadly, 27018 covers one narrow thing well: protecting personally identifiable information (PII) in public clouds where the provider acts as a PII processor. That brings consent, purpose limitation, disclosure of any subprocessors, transparency about where data is processed and stored, and deletion once the relationship ends into scope.
It’s the natural fit for public cloud providers who want a recognized privacy control set that maps cleanly onto GDPR’s processor obligations.
8. CSA STAR and the Cloud Controls Matrix
The Cloud Security Alliance maintains both pieces here, and they’re easy to blur together. The Cloud Controls Matrix is the control framework itself. STAR is the assurance program built on top of it. CCM v4.1 came out in late January 2026 with 11 new controls, bringing the total to 207 across the same 17 domains.
STAR runs three levels. Level 1 is a free self-assessment built around the CAIQ questionnaire, published to a public registry anyone can browse. Level 2 adds independent third-party assessment, often run alongside an ISO 27001 or SOC 2 engagement already underway. CSA also describes a Level 3 built around continuous auditing, but the Registry listings you’ll actually run into are Level 1 and Level 2.
The practical value sits in the registry itself. If you’re evaluating a cloud provider that has published to STAR, its CAIQ answers are right there in public, specific enough to check against the rest of its evidence. Just remember that Level 1 answers are self-reported.
9. NIST SP 800-53 (Release 5.2.0)
NIST publishes this one as a control catalog rather than a certification, and it’s the source material behind FedRAMP’s baselines along with a lot of private-sector control mapping.
Release 5.2.0 landed on August 27, 2025, and anyone who owns patching should read it. Issued in response to a federal executive order on software update security, it added a root cause analysis enhancement for system issues and failures, which covers failed updates (SI-02(07)), a logging syntax enhancement (SA-15(13)), and a new cyber resiliency design control (SA-24).
The update treats the patch pipeline itself as an attack surface worth securing, not just the vulnerabilities that pipeline exists to fix.
10. NIST Cybersecurity Framework 2.0
NIST publishes this one too, and version 2.0 arrived in February 2024. It’s voluntary guidance with no certification track and no auditor to satisfy.
CSF 2.0 added a sixth function, Govern, alongside the original five: Identify, Protect, Detect, Respond, and Recover. It also broadened the scope beyond the critical infrastructure focus that shaped version 1.1, and now targets organizations of any size or sector.
Think of it as the org chart for your security program, with the detailed controls from 800-53, CIS, or CCM mapped underneath it. CSF is weak at telling you what to configure and strong at telling you what you forgot to assign an owner to.
11. FedRAMP
Run by the FedRAMP PMO under GSA, FedRAMP authorizes cloud services for use by US federal agencies, and 2026 brought its biggest overhaul in years.
FedRAMP launched the Consolidated Rules for 2026 in late June. They took effect on July 4, 2026, which opened an early adoption phase, and FedRAMP 20x is set to replace Rev5 over time. The vocabulary changed along with the structure. “Authorization” became “FedRAMP Certification,” impact levels gave way to certification Classes A through D, and providers no longer keep Plans of Action and Milestones. They maintain vulnerability records and a list of Accepted Weaknesses instead, while agencies can still open their own POA&Ms for agency-owned actions and risk decisions.
Which dates matter depends on where you stand. If you already hold a Rev5 certification, the Consolidated Rules become mandatory on January 1, 2027, though some rulesets carry their own effective dates and grace periods, and the last of those grace periods ends on February 1, 2028. If you’re still planning a Rev5 application, FedRAMP stops accepting new ones on June 11, 2027, and after that, the only route is a 20x certification. If your documentation still says “FedRAMP Moderate ATO,” that’s Rev5 terminology, and the deadline that applies to you is January 1, 2027, when the Consolidated Rules become mandatory. There’s time, but not a lot of it.
FIPS-validated cryptography still matters here, though the new rules narrow its scope. FedRAMP now expects FIPS 140 encryption to protect sensitive data and wants providers to document where they use it, so agencies can judge the fit for their own systems. On AlmaLinux, TuxCare Enterprise Support delivers FIPS-compliant updates for the full FIPS package set (kernel, OpenSSL, libgcrypt, NSS, and GnuTLS) through Extended Security Updates for select minor versions. AlmaLinux 9.2 and 9.6 both carry active CMVP certificates for all five modules, the most recent issued in August 2026.
12. NIS2 Directive
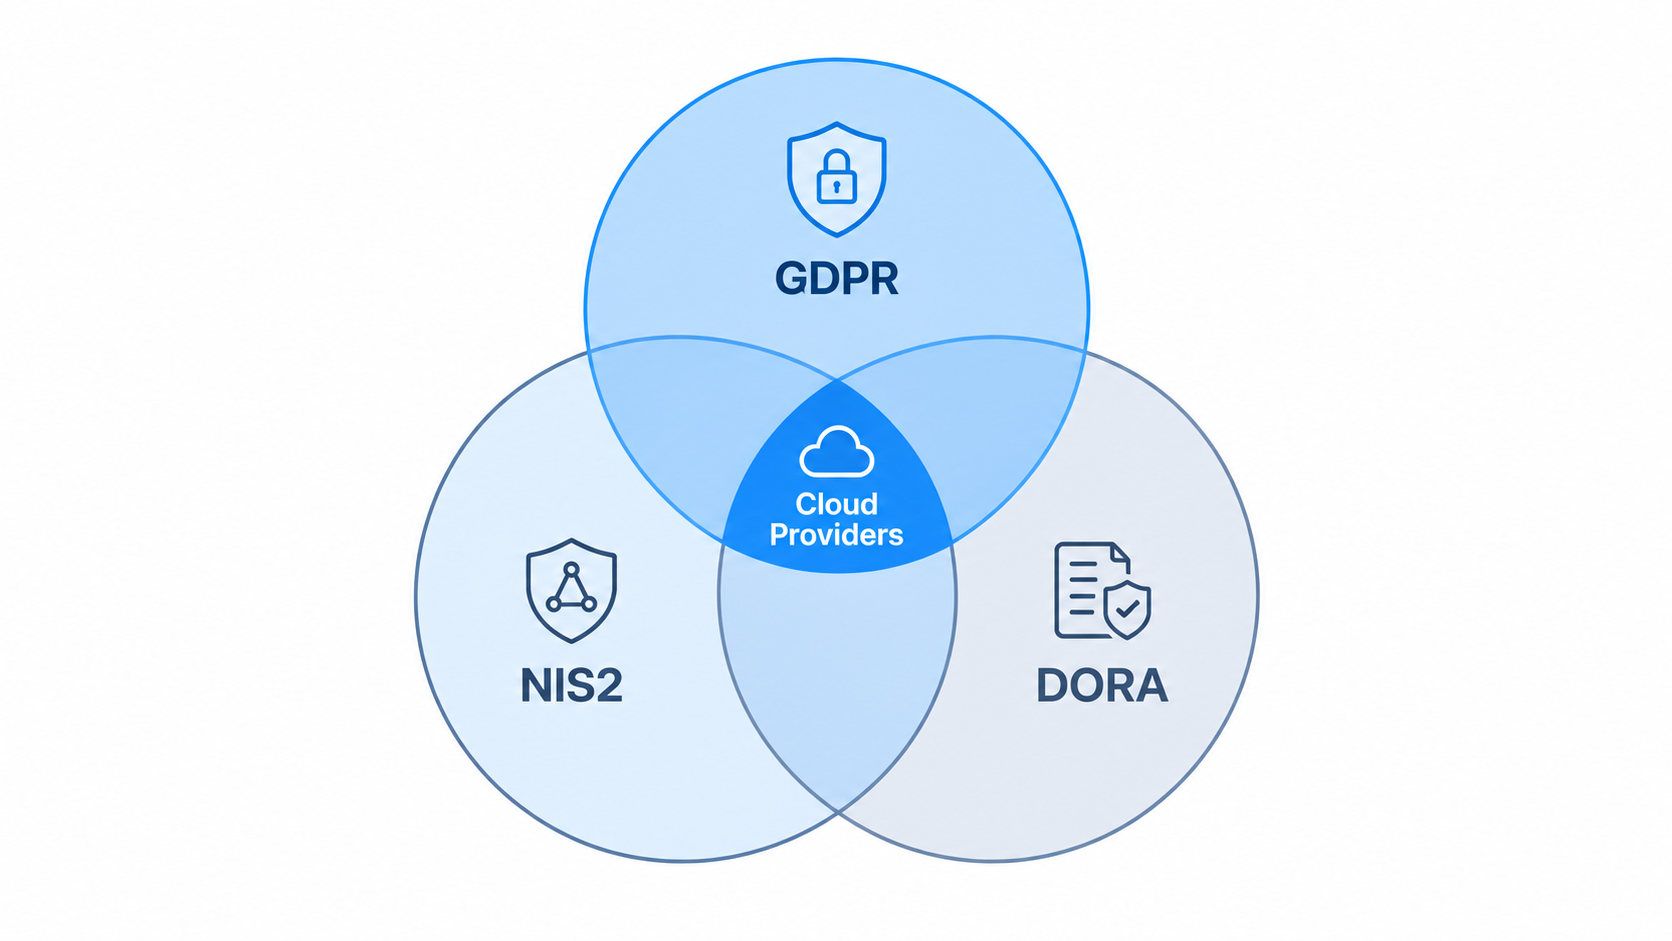
NIS2, formally Directive (EU) 2022/2555, works differently from a regulation because it’s a directive. The directive binds the member states, but the obligations on companies only arrive once each state transposes it into national legislation, and that process has gone unevenly across the bloc.
The transposition deadline was October 17, 2024. In July 2026, the European Commission referred Ireland, Spain, France, and the Netherlands to the Court of Justice of the EU for failing to notify full transposition, and asked the court to impose financial sanctions. The Netherlands brought its Cybersecurity Act into force on August 15, 2026, and as of mid-September, Ireland, Spain, and France were still working on theirs. Because NIS2 is a directive, obligations on private entities depend on each state’s national implementing law, so check the applicable domestic statute rather than assume uniform direct effect. NIS2 requires member states to make management bodies accountable under national law, and national rules have to allow fines for essential entities of at least EUR 10 million or 2% of worldwide annual turnover, whichever is higher.
NIS2 covers entities in 18 sectors, including cloud computing providers, data center services, and managed security service providers.
13. DORA
The Digital Operational Resilience Act, Regulation (EU) 2022/2554, entered into force in January 2023 and became fully applicable on January 17, 2025. The European Supervisory Authorities coordinate its implementation.
DORA applies directly to financial entities across the EU and is built around five pillars: ICT risk management, incident reporting, digital operational resilience testing, ICT third-party risk management, and information sharing.
The third-party pillar is the one cloud providers tend to overlook. Financial entities have to push DORA’s requirements into their ICT contracts, and a provider designated as a critical ICT third-party provider comes under direct oversight from a Lead Overseer drawn from the ESAs. That means selling infrastructure to EU banks can pull you into DORA’s reach even though you’re not a financial entity yourself.
14. CIS Benchmarks and CIS Controls v8.1
The Center for Internet Security publishes two related resources here: the Controls, a prioritized set of safeguards, and the Benchmarks, which are platform-specific configuration baselines. Neither one is certifiable in the traditional sense.
CIS Controls v8.1, released in June 2024, organizes 18 prioritized controls into three Implementation Groups based on risk, resources, and complexity, so a small team and a large enterprise aren’t held to identical starting expectations. CIS Benchmarks are the configuration-level counterpart: hardening guides written for specific platforms, including AWS Foundations, Azure Foundations, GCP, Kubernetes, and major Linux distributions.
Benchmarks are where standards stop being abstract and start telling you which setting to change. Plenty of cloud posture management tools ship CIS Benchmark checks out of the box, which makes them one of the easiest starting points on this list.
For AlmaLinux, TuxCare Enterprise Support includes security hardening help that maps CIS and STIG controls to compliance frameworks such as PCI DSS and ISO 27001.
Best Practices for Cloud Security
Standards tell you what to prove. These five practices are how teams actually produce the evidence.
Regular Security Assessments
Run assessments on a defined cadence rather than only when an auditor comes calling. Cadence varies by standard – some spell out annual cycles, others are risk-based with no fixed interval. PCI DSS Requirement 12.5.2 adds an annual scope-confirmation exercise on top of whatever cadence you choose.
The economics favor sticking with it. IBM’s 2026 Cost of a Data Breach Report puts the global average breach at USD 4.99 million, a 12% jump and a new record that reverses the previous year’s brief decline.
Scope drift is the failure mode worth watching for. Picture a 40-person SaaS team that spins up a staging environment for a migration, forgets to decommission it, and leaves it sitting outside the assessed boundary for months.
If an assessment finds nothing at all, the scope is probably drawn too narrowly. If it finds the same three issues every quarter, the problem sits in remediation ownership rather than detection.
Vulnerability Scanning
Run authenticated scans from inside the environment, on top of any external scanning. Unauthenticated external scans miss package-level vulnerabilities in running workloads, which is where a lot of the exploitable stuff actually lives.
Minimum cadence varies a lot by standard. PCI DSS wants internal and external scans every three months and after any significant change, and the required external scans have to go through an Approved Scanning Vendor. DORA’s technical standards call for automated vulnerability scanning at least weekly on ICT assets supporting critical or important functions, yearly testing of the systems behind those functions, and threat-led penetration testing at least every three years for the entities their regulators designate. The proposed HIPAA update would require automated scans at least every six months and penetration testing at least once a year. CIS Controls v8.1 asks for automated scans of internal assets at least quarterly (Safeguard 7.5) and of externally exposed assets at least monthly (Safeguard 7.6). NIS2 stays risk-based and leaves the specifics to each member state.
Cross-reference findings against the CISA Known Exploited Vulnerabilities catalog before prioritizing remediation. A CVSS score alone will bury an actively exploited 7.5 under a pile of theoretical 9.8s with no known exploitation.
The cadence rules above assume a scanner accurately reports what’s already fixed, and on Linux that assumption breaks down often. Distributions backport security fixes without changing the upstream version number, and a rebootless patch applied in memory may not show up in a package-version check at all. TuxCare Radar checks actual patch status, including rebootless patches and ELS-covered fixes that a plain version check would miss, so a scan cycle doesn’t turn into a manual reconciliation between what the scanner says and what your patch logs say.
Strong Access Controls
Enforce multi-factor authentication on every human account with console access, with no exceptions for service owners or contractors. PCI DSS v4.x extended MFA beyond administrators to all access into the cardholder data environment, with a narrow exception for accounts that use phishing-resistant authentication, and the proposed HIPAA update heads the same way.
Beyond MFA, make least-privilege, role-based access the default and review it at least quarterly. Keep human and machine identities separate, with no shared service account credentials living in CI pipelines. Choose short-lived credentials over long-lived API keys wherever the provider supports them. And document your joiner-mover-leaver process, because auditors routinely sample it.
Data Encryption
Encrypt data at rest and in transit as a baseline expectation. Key management is the part that actually fails audits: who holds the keys, how often they rotate, and whether you can show exactly what the provider can and can’t decrypt.
For regulated workloads, the implementation matters as much as the algorithm choice itself. US federal systems generally require FIPS 140-3 validated cryptographic modules wherever approved cryptography is mandated, and commercial contracts increasingly ask for them as well. TLS 1.2 is the floor, and TLS 1.3 is the goal wherever your stack supports it.
Watch Out: Encryption at rest with provider-managed keys checks a lot of compliance boxes, but what it really protects against is storage-layer exposure, like a stolen disk or badly retired media. It does nothing against a compromised credential inside your own account that’s allowed to decrypt. Auditors rarely push on this distinction. Attackers routinely exploit it.
Regular Patching and Updates
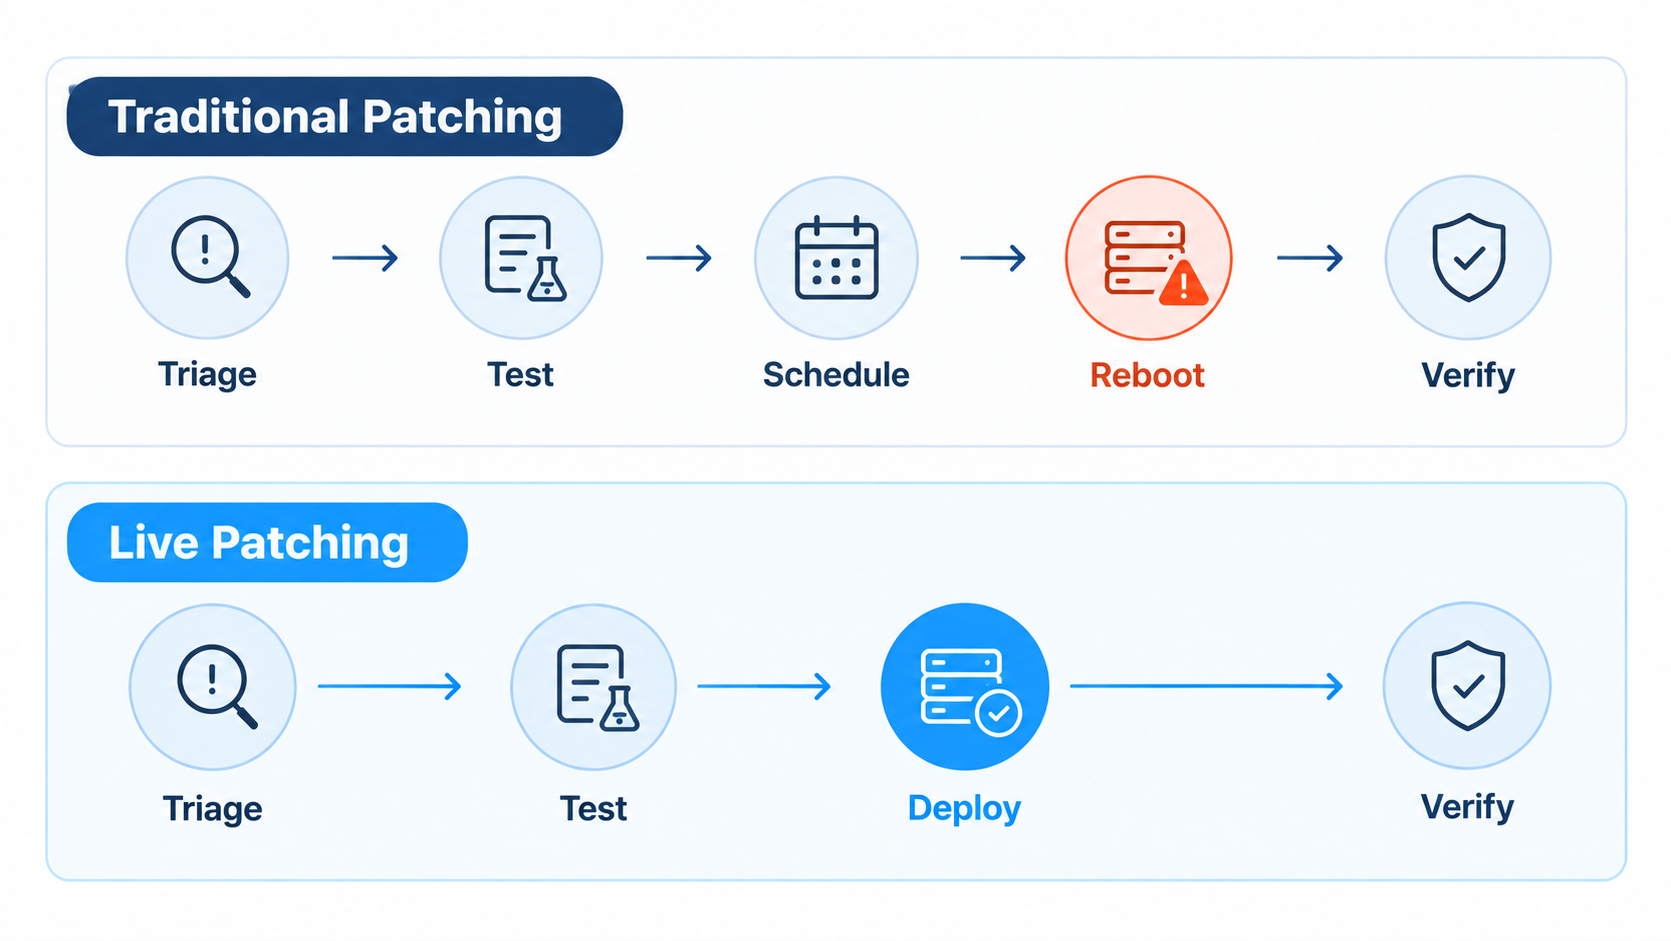
This is where most cloud compliance programs quietly come apart. The controls read simply on paper and prove hard to operate in practice, because patching a production kernel usually means a reboot, and a reboot means negotiating a maintenance window with everyone who depends on that uptime.
The clock is explicit across several standards:
| Standard | Patch requirement |
| PCI DSS v4.0.1 | Critical patches within one month of release, other applicable patches on an entity-defined, risk-based timeframe (Req. 6.3.3) |
| NIST SP 800-53 | Flaw remediation within organization-defined timeframes (SI-02) |
| CIS Controls v8.1 | Automated OS and application patch management, monthly or more often (Safeguards 7.3 and 7.4) |
| NIS2 / DORA | No universal numeric deadline, with remediation timing driven by each regime’s risk and vulnerability management requirements (see Vulnerability Scanning above for DORA’s scanning and testing cadences) |
| HIPAA (proposed) | Critical-risk patches within 15 calendar days and high-risk patches within 30, with other patches on a policy-defined timeline |
A 30-day window sounds generous until you count the actual steps involved: triage, test, schedule, notify, reboot, verify, document. Across a fleet of a few hundred hosts with uptime SLAs to honor, that can eat most of the month before the patch ever touches production.
Final Thoughts
Pick your standards by obligation first, then by buyer demand, and stop there. Running ISO 27001, SOC 2, and CSA STAR all at once because a competitor’s trust page lists all three is how small security teams burn a year on documentation instead of controls.
One thing holds no matter which standards apply to you. Nearly all of them expect you to find and fix known vulnerabilities, and to have evidence you can produce on demand. Certification type varies. Enforcement varies. But for most of these programs, patching operations are where that evidence either gets produced on schedule or slips.
Endless Lifecycle Support keeps security updates flowing to end-of-life operating systems, language runtimes, and libraries after vendor support ends, so an unsupported component can keep getting fixes instead of becoming a lasting compliance gap. For the open source dependencies your cloud workloads pull in, SecureChain gives teams screened private registries for JavaScript, Python, Java, Go, Rust, and PHP packages, which supports the kind of supply chain controls ISO/IEC 27017 and CCM v4.1 describe. TuxCare Enterprise Support covers the FIPS-validated cryptography and compliance hardening that federal and other regulated environments often ask for. And KernelCare applies kernel patches without a reboot, so meeting the deadlines PCI DSS and similar standards set doesn’t hinge on a maintenance window getting approved. You still test, verify, and document like any other patch, but the reboot drops out of the schedule.
Have questions about which of these standards apply to your environment, or where your compliance program’s evidence gaps actually sit? Talk to a TuxCare security expert.