
 Tech Support
 Documentation
 Login
 Contact Us


Go straight to an AI summary of this blog post instead 


Uh oh – you asked an LLM to generate your Dockerfile, and now you’re staring at an error about Node. Turns out the base image it gave you includes a version of Node with known vulnerabilities. Not exactly what you had in mind when trying to save time.
Don’t worry, though – this is a common issue when using AI tools for boilerplate code like Dockerfiles. The good news? It’s easy to fix, and we’ll walk you through exactly how to swap out that vulnerable Node version for one that’s secure and up to date. Let’s get this sorted.
What in Tarnation!?!
I thought using AI and LLMs was the best way to go for something as straightforward as a Dockerfile. I mean, everything is AI these days, and AI is supposed to be really good at this stuff…
That’s exactly what I was thinking. With AI everywhere and companies seemingly only hiring “AI unicorns,” it’s easy to jump in headfirst – until it bites back. It sure did for me when my shiny, AI-generated Dockerfile started throwing errors.
Luckily, we can fix this – the old-school way, with just a bit of human touch.
I Curse the Day You Were Born, LLM!
Let’s say you’re a newer developer stepping into the Docker world, trying to deploy your first app in a container. Naturally, you might turn to Copilot, Claude, or another LLM to help whip up a Dockerfile.
Let’s be real – if you’re like me, a frontend dev who’s barely dipped a toe into DevOps, you probably have no idea what’s actually supposed to go in that Dockerfile. There’s a whole mess of stuff you could configure. That’s where an LLM steps in to save the day… or so you think.
Oops… This Dockerfile Has a Node Vulnerability Built In
So here’s what happened: I asked Claude to help me write a Dockerfile for a little Next.js app I’ve been messing around with. It’s not fully built yet, but I figured it’d be a good time to try containerizing it, just to see if I could actually pull it off.
Docker’s already installed on my machine, so that part was good to go. The next step was figuring out how to actually write the Dockerfile… and naturally, I turned to AI for a little help.
When Claude generated the Dockerfile for me, I noticed something right away. The base image it suggested was Node 18. Here’s that part of the file – honestly, the rest doesn’t really matter for this conversation:
# Use the official Node.js runtime as the base image

FROM node:18-alpine AS builder
And wouldn’t you know it, the moment I opened the file in Visual Studio Code, I got hit with an error. Turns out the Node version in that image — Node 18 — has a known security vulnerability. Not great.
VS Code was kind enough to throw a warning and even point me toward Docker Hub, where I could read more about the issue. It basically told me, “Hey, buddy… maybe don’t use this outdated Node version because it’s got vulnerabilities baked right in.” Yikes.
Learn more about the security vulnerability on Docker Hub.
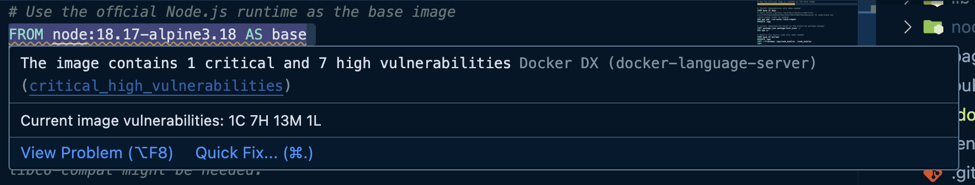
Now, this is a pretty big deal. If you’re building anything – even if it’s just for learning or testing – you really don’t want to be shipping stuff that’s running on insecure foundations. Vulnerabilities in your base image are one of those sneaky things that can quietly open the door to all kinds of headaches down the line.
Thankfully, the fix is about as simple as it gets.
How I Fixed It (and You Can Too)
Alright, so how do we fix this mess? Honestly, the error in VS Code pretty much hands you the answer on a silver platter. You can click Quick Fix or even ask Copilot to explain it, and it’ll come back with something along the lines of:
“…and to address the high vulnerability in the base image, update the Node.js image to a more secure version.”
Translation? Stop living in the past. Update to the latest Node version.
So, that’s exactly what I did. I swapped out Node 18 for Node 22 — the most current stable version as of today. Here’s what the updated line looks like now:
FROM node:22-alpine31 AS base
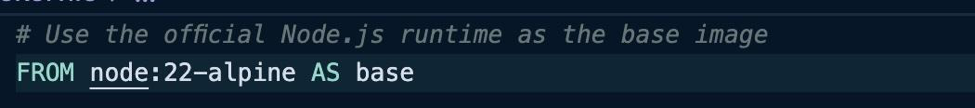
And like magic – no more errors. Everything built cleanly, the vulnerability warning disappeared, and the container spun up without a hitch. I fired it up in Docker Desktop, navigated over to localhost, and there it was – running exactly like it should.
This whole thing was a nice little reminder that, while AI tools are awesome for helping you move faster, they’re definitely not perfect. You still need that ✨ Human Touch ✨ to catch these kinds of issues and make sure what you’re building is secure and production-ready.
Now go forth, update those base images, and keep your containers happy and healthy!

