
 Tech Support
 Documentation
 Login
 Contact Us

1
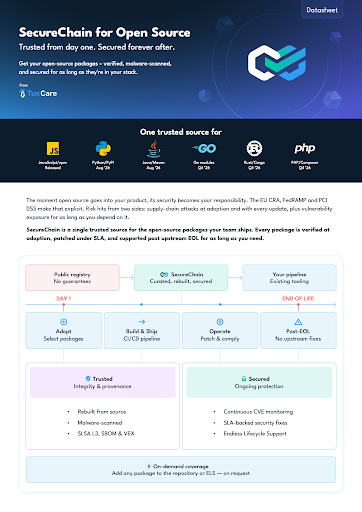
trusted source for every
package across your stack
6
ecosystems secured from
install through post-EOL
100%
rebuilt packages from
verified source
This datasheet tackles questions like:
Which path best fits your priorities – upstream, in-house, or a trusted source
What each option actually delivers in practice – beyond vendor positioning
Where security and compliance gaps emerge after adoption
How cost and risk evolve across each approach
What impacts your open-source supply chain the most – and what doesn't
How to stay secure and compliant without forcing a costly rebuild
(and many more! )
Why should you read this datasheet?
Why should you read this datasheet?
You’ll get a clear, side-by-side view of your options – grounded in real delivery models, risks, and outcomes. If you’re responsible for open source, security, or long-term platform strategy, this guide shows where the trade-offs really are and how to approach them with confidence.