
 Tech Support
 Documentation
 Login
 Contact Us

7 Days
mainstream patch SLA for Critical vulnerabilities once an upstream fix is available
3 Months
of sustained patching that begins the moment upstream goes quiet
No Gap
between SecureChain and ELS
coverage when both licenses
are in place
This datasheet tackles questions like:
What happens when upstream never declares end of life and simply stops fixing vulnerabilities?
When does a component move from Mainstream coverage into Sustained support (and who decides)?
How long does SecureChain keep patching after upstream support ends, and when does ELS take over?
How quickly are Critical, High, Medium, and Low severity vulnerabilities patched at each stage?
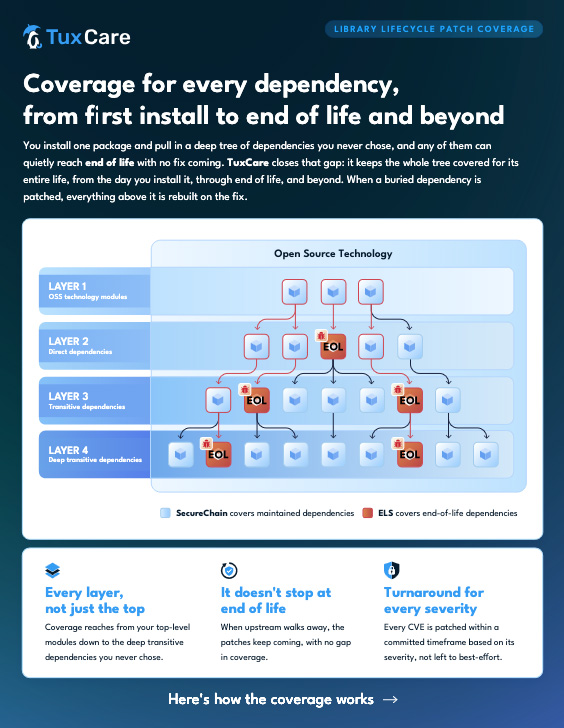
How far does coverage reach down the dependency tree, including deep transitive dependencies?
Can SecureChain and ELS cover the same component with no uncovered day between them?
(and many more! )
Why should you read this datasheet?
Because “supported” can mean very different things depending on where a component sits in its lifecycle, and most component risk isn’t something you introduce – it’s something you inherit when someone else stops working.
This datasheet shows what happens before, during, and after upstream support ends: the point where TuxCare steps in, how long coverage continues, and what you need in place to keep patches arriving without a lifecycle gap. No re-platforming, no forced upgrade. The version you’re running stays yours.