Tech Support
 Documentation
 Login
 Contact Us


Go straight to an AI summary of this blog post instead 


Key Takeaways
- Live kernel patching, also known as rebootless patching, fixes security vulnerabilities in a running Linux kernel without requiring a reboot.
- Automated live patching allows critical security updates to be applied immediately while maintaining continuous system availability.
- Enterprises use rebootless patching to reduce exposure windows, avoid downtime, and meet uptime and compliance requirements.
- TuxCare’s KernelCare provides automated rebootless patching for most enterprise Linux distributions.
Breakthroughs don’t often happen in cybersecurity, but, when one does, it can be a real magic bullet. Linux kernel live patching is one of those incredible cybersecurity breakthroughs that truly changed the game in the fight against threat actors.
But what exactly is rebootless kernel patching, how does it benefit IT teams and the broader organization, and what is the future of live patching? Continue reading our comprehensive breakdown on live patching to find out.
What Is Live Kernel Patching?
Rebootless Linux kernel live patching is the ability to apply a security patch to a live, running kernel without rebooting. It is a modern approach that eliminates the downtime issues related to conventional patching practices.
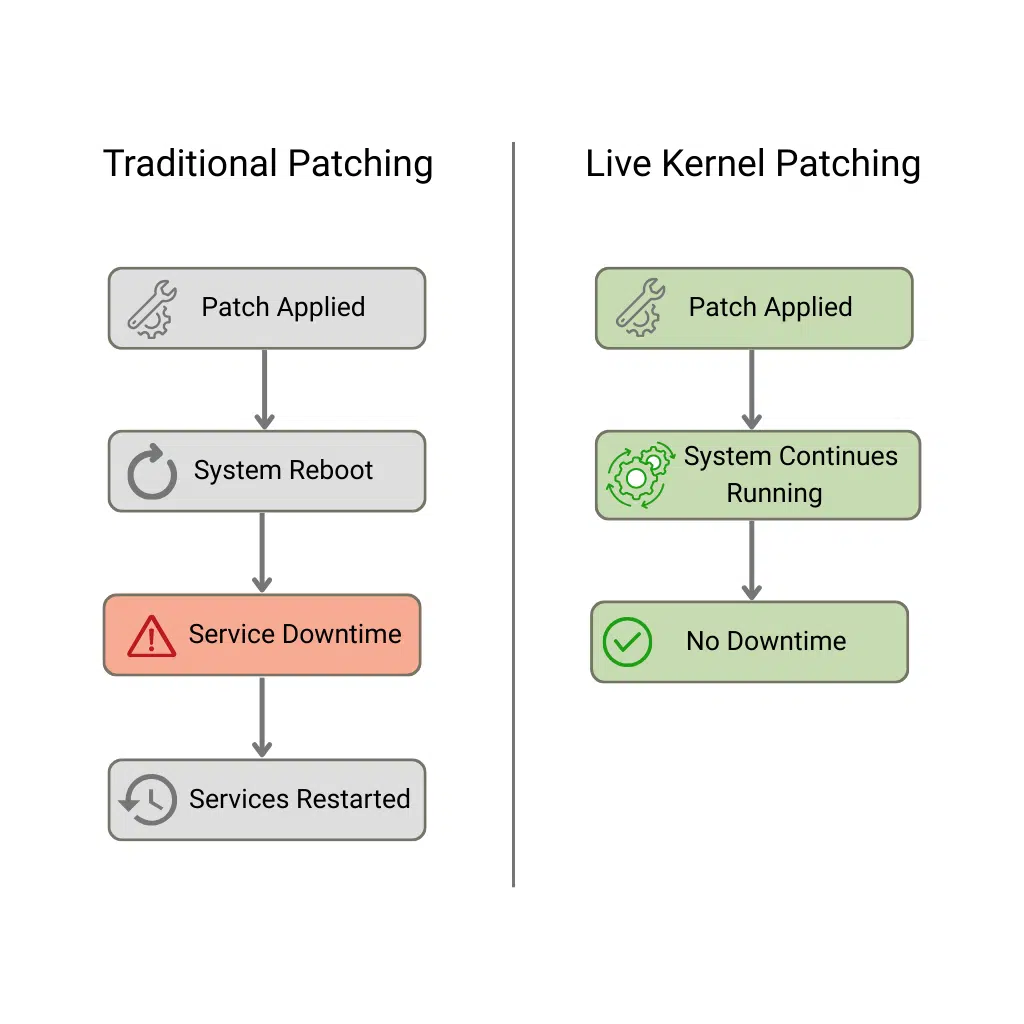
Patching kernels with traditional methods often involves restarting systems, which leads to service disruption. For mission-critical environments that need 24/7 uptime, traditional patching is simply not a viable solution.
Because live patching is so responsive (remember, no maintenance schedules and no downtime), it means that patches are applied consistently and that there are no “window periods” where attackers can exploit a published vulnerability.
The Cost of Delay: A 2022 survey by TuxCare shows that 55 percent of respondents attributed a data breach to their organization’s failure to apply an available patch for a known vulnerability.
The History of Linux Kernel Live Patching
It was a researcher whose unpatched Linux server got hacked – Jeff Arnold, at MIT – who started research into live patching in 2006. What motivated him? Well, Arnold’s Linux server was hacked because he delayed a key security update, as he didn’t want to inconvenience other people. It was obvious to him that enterprise Linux users needed an alternative patching method.
Research at MIT was the first stepping stone into rebootless kernel patching. Jeff and some of his colleagues founded a company called KSplice, Inc., which was acquired by Oracle in 2011. Other organizations followed when Red Hat and SUSE also led efforts to develop live patching for Linux servers with their respective solutions, Kpatch and kGraft, which were later combined into a single product.
How Does Live Kernel Patching Work?
Live patching is a simple premise, but there is a bit of complicated, technical gymnastics going on in the background.
Here’s a simplified explanation of how it works:
The live patching service creates a rebootless patch from the corrected code so that the corrected code can be loaded into the running kernel memory. Code execution is then redirected away from the vulnerable version of the code to the corrected version of the code while the kernel is running.
It means that the kernel does not have to be restarted, which also means that the whole system avoids a reboot. Nonetheless, even though the system was never rebooted, the corrected version of the code is now used and the system is safe from the vulnerability.
The patch can be as complex or as simple as necessary. From a single one-line fix to multiple functions, the process is always the same. It’s a bit like magic, and live kernel patching has major practical implications for day-to-day, on-the-ground patching efforts.
Without live patching, system administrators must plan and schedule maintenance windows to take enterprise Linux servers offline. For large technology estates, it is a complicated process that is bound to upset someone, somewhere along the way, because nobody likes downtime.
Benefits & Importance of Live Kernel Patching
When you bring live patching software into the picture, servers and applications no longer need to go offline for patching. And, system administrators do not need to worry about maintenance schedules, nor do stakeholders ever hear the words “downtime” or “disruption”.
What follow are the key benefits of Linux kernel live patching.
1. Continuous Security
Multiply the patching puzzle across thousands of machines, and take into account the emergence of thousands of vulnerabilities every year, and you’re quickly stuck with a tough problem: stakeholders just won’t tolerate disruption and revenue loss every time a patch needs to be applied.
That, in turn, means patches are applied less frequently than the ideal.
Organizations schedule downtime for patching at a pace of, say, once a month – if they’re doing a good job. That means there are significant window periods between when a vulnerability is identified in public, and when a patch is finally applied.
Thanks to the ability to apply a no-reboot kernel live patch, there’s no waiting period for maintenance windows and no interruption to running services.
2. Zero Downtime and High Availability
Reboots and the associated Linux server downtime lead to delayed patching. Take away the maintenance window requirement (and the resource drain caused by rebooting) and you solve a big chunk of the patching problem.
When you force a reboot, you’re temporarily taking services offline, which is a nightmare for business operations and customer access. Live kernel patching keeps systems running while security fixes are applied. For anyone running high-traffic servers or 24/7 cloud deployments, this rebootless patching approach helps maintain availability and avoid the costs that usually come with planned downtime.
3. Operational Efficiency
Rebootless patching has big, positive, practical implications for tech teams as well.
Because kernel updates happen automatically in the background, system administrators can spend their time doing higher-level tasks that contribute to overall security posture.
It implies happier stakeholders too, because maintenance windows have a way of upsetting everyone in the organization. Downtime means disrupted revenue streams, unhappy customers, and frustrated employees. Live patching significantly reduces these problems by removing the need for frequent maintenance windows.
4. Compliance and Regulatory Readiness
The consistent, gapless nature of live patching has an important implication in today’s highly regulated world, and live patching is a game-changer for organizations that have compliance obligations. For example, take the PCI DSS (Payment Card Industry Data Security Standard), which applies to organizations that process payments.
PCI DSS demands in Section 6.2 of its rules that critical security patches are applied within a month of release. Patch later than that and you fall foul of PCI DSS requirements – which can have significant consequences, including heavy fines, or worse, if a breach occurs. Standards such as ISO 27001 and the the NIST Cyber Security Framework have similar requirements for patching.
Pro Tip: Organizations that use live kernel patches reduce the risk that they break compliance rules to the minimum because patching no longer relies on manual intervention or unreliable and lengthy maintenance windows. Whatever compliance timeframe you’re required to meet is automatically achieved.
Are there any negatives to Linux kernel live patching?
Live kernel patching solutions are often tied to a single enterprise Linux distribution and are often available only through vendor-specific, expensive support contracts.
At TuxCare, we’ve independently developed the patented KernelCare live patching solution for almost a decade, supported by the team at CloudLinux. KernelCare enables rebootless kernel patches to be applied across all major enterprise Linux distributions, providing a universal and affordable live patching service that is not restricted to a single vendor ecosystem such as Red Hat or SUSE Linux.
Live patching isn’t free, so there is an important cost factor to keep in mind when signing up for a live patching service. For Kpatch and other vendor-sponsored live patching services, the costs can be significant, as live patching is included in support plans. Consider the price tag of $1,299 per machine, per year for Red Hat Premium Support, for example.
By comparison, TuxCare’s KernelCare live patching is affordable, at just $49.50 per year, per machine. It’s a small price to pay when you consider the time saved trying to organize maintenance windows and patch vulnerabilities manually. That’s not to mention the potential cost of a successful cyber-attack that occurred because you failed to patch.
What’s more, KernelCare introduced persistent live patching. The original method for live patching, called temporary live patching, led to reduced performance over time because patches are applied using a technique that accumulates patches on top of one another.
In contrast, persistent live patching contains a cumulative fix in one binary, so there’s no performance drag. KernelCare has removed the performance concern, as systems are simply patched while they’re running – and then continue running just as before, with no performance hit.
Popular Live Kernel Patching Tools
There are multiple live patching tools available from different providers. Most are provided by the Linux distribution vendor itself and are designed to work only with that specific distribution.
KernelCare
TuxCare’s KernelCare is a vendor-independent live patching solution that supports a wide range of enterprise Linux distributions, including RHEL, CentOS, AlmaLinux, Rocky Linux, Ubuntu, Debian, Oracle Linux, CloudLinux, Amazon Linux, and more. It enables automated deployment of kernel patches without reboots or maintenance windows.
Key Features
- Supports all popular enterprise Linux distributions
- Offers up to 100% CVE coverage for supported kernels
- Available for both x86-64 (Intel and AMD) and ARM64 architectures
- LibCare extends live patching to shared libraries such as glibc and OpenSSL
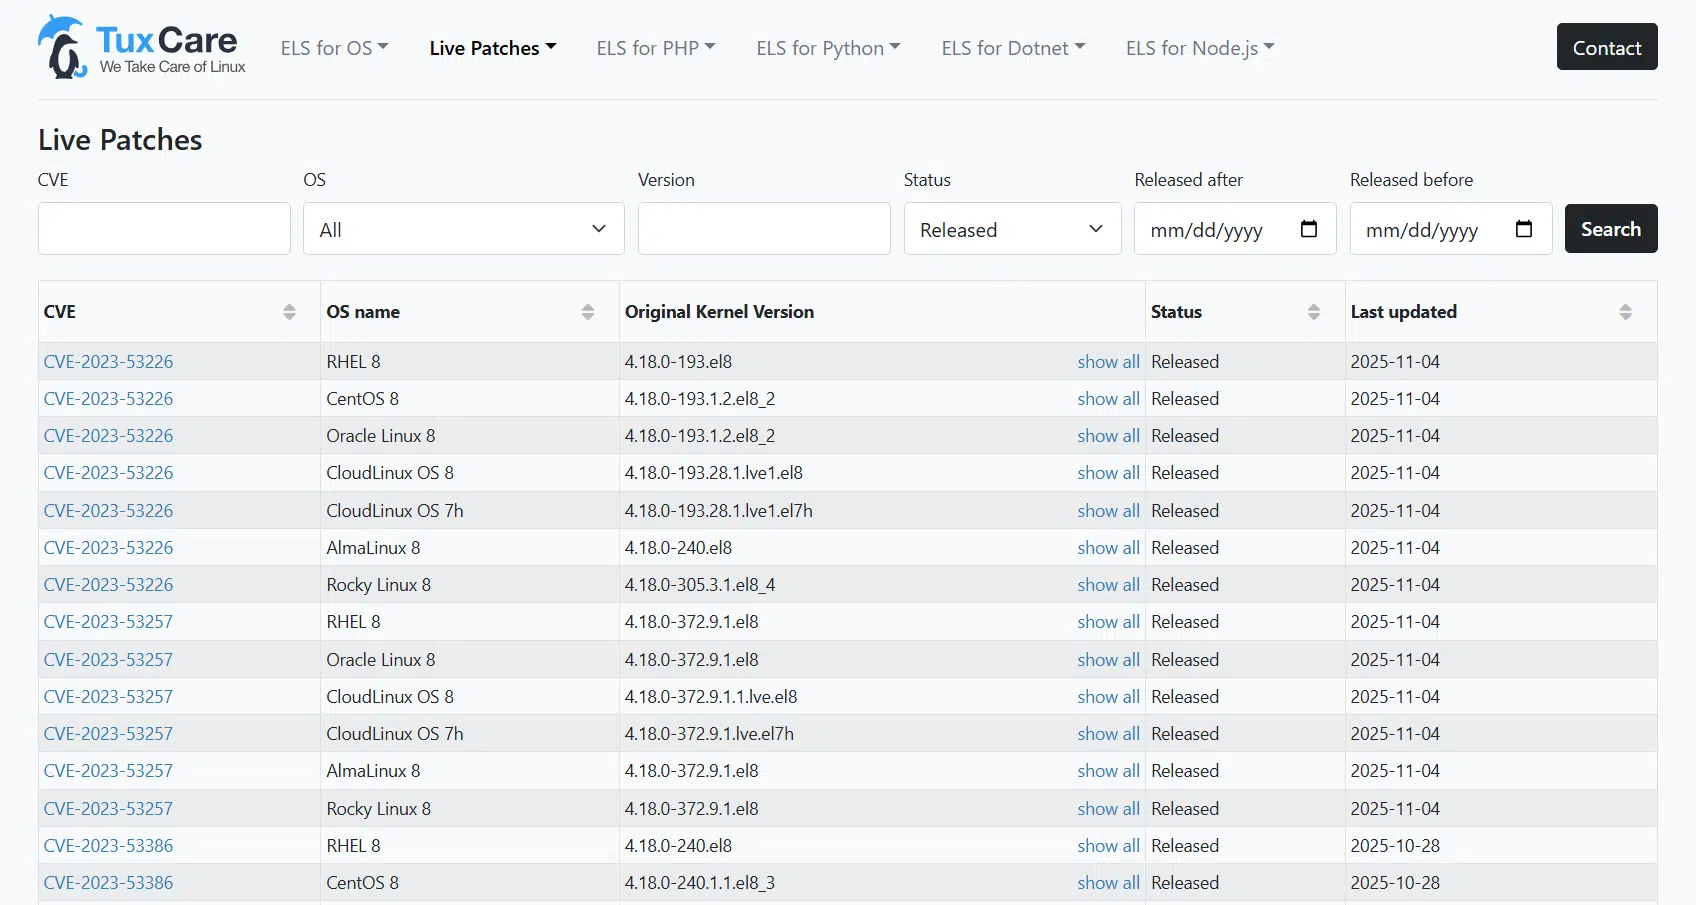
You can monitor KernelCare live patches for kernel vulnerabilities in TuxCare’s CVE tracker.
Oracle Ksplice
Ksplice originated as an academic project at MIT and was later acquired by Oracle. It is now the built-in live patching mechanism for Oracle Linux.
Focus: While Ksplice can support other distributions like RHEL, CentOS, and Ubuntu, Oracle’s main focus is providing patches for Oracle Linux environments, often tightly integrated with their own kernel variants.
Limitation: It is generally available only to customers with an Oracle Premier Support subscription.
See the full breakdown: KernelCare vs Ksplice
kpatch (Red Hat)
kpatch is the native live kernel patching technology developed and maintained by Red Hat. It is the default solution for Red Hat Enterprise Linux (RHEL) and CentOS Stream.
Focus: It focuses on patching kernels built and maintained directly by Red Hat.
Limitation: It is typically limited to the specific kernel versions supported by Red Hat and its derivatives, and it does not inherently support other distribution families.
See the full breakdown: KernelCare vs kpatch
kGraft (SUSE)
kGraft is the live kernel patching implementation developed by SUSE. It is the native solution for SUSE Linux Enterprise Server (SLES).
Focus: Similar to kpatch, kGraft is optimized for and bundled with SUSE’s enterprise distribution, ensuring compatibility within that ecosystem.
Limitation: It is great if you only run SUSE, but less ideal for mixed environments.
Livepatch
Canonical Livepatch is the native live kernel patching service for Ubuntu, designed to keep LTS versions of Ubuntu secure without reboots.
Focus: It is integrated into the Ubuntu Pro subscription, making it easy to manage for Ubuntu-only infrastructures.
Limitation: It only works on Ubuntu. If your infrastructure includes other distros like AlmaLinux or CentOS, you’ll find yourself managing multiple different patching tools.
See the full breakdown: KernelCare vs Livepatch
Keeping Linux Systems Secure with Rebootless Patching
Live security patching is a major win for cybersecurity. It makes light work out of applying kernel patches to Linux enterprise servers, a task that’s typically a tough, time-consuming practice.
If you run enterprise Linux workloads such as Red Hat or Oracle Linux, rebootless live kernel patching is worth evaluating as part of a modern security strategy.
TuxCare’s live patching solution has now expanded beyond the kernel to include a wide range of live patching services – covering critical shared libraries with LibCare and embedded and IoT environments with KernelCare IoT.
Learn more about TuxCare’s rebootless patching solutions.