
 Tech Support
 Documentation
 Login
 Contact Us


Go straight to an AI summary of this blog post instead 


Key Takeaways
- End-of-life (EOL) software no longer receives security updates, leaving systems vulnerable to known threats.
- Running end-of-life software increases security risks, compliance issues, and operational disruptions.
- TuxCare provides vulnerability patches for EOL open-source software to help you stay secure and compliant.
Many businesses continue using software past its end-of-life date, often without realizing the risks. Unsupported software exposes systems to cyberattacks, compliance failures, and operational downtime.
In this article, we explore the dangers of running EOL software, the importance of security updates, and practical steps organizations can take to stay secure even after vendor support ends.
What Is End of Life Software?
End of Life (EOL) software refers to operating systems or applications that are no longer maintained by the vendor. This means the vendor stops providing security updates, bug fixes, and official support. While EOL software may still function, it creates major security risks since any vulnerabilities discovered after the end-of-life date will not be resolved.
Most software follows a lifecycle where support is phased out after a set period. For example, Ubuntu LTS releases receive 5 years of standard support before entering extended maintenance, which precedes their end of life.
What is EoS and EoSL in Software?
Vendors use specific terms to describe the end of a product.
|
Term |
Meaning |
|
EoS (End of Support) |
Free updates typically stop. Some vendors offer paid extended support. |
|
EoSL (End of Service Life) |
All support ends and the software is fully abandoned. The vendor no longer helps. |
Note: Using EOL software can be a significant risk to an organization’s system and its security, so it’s essential to keep software up to date with the latest security patches and updates to avoid potential security breaches.
Software Categories That Reach End of Life
End of life does not describe a software “type.” It describes a support state. Still, EOL most often affects certain software categories, each with different risks.
Operating Systems
When an OS reaches EOL, vendors stop shipping kernel and system security fixes. This leaves known vulnerabilities unpatched and increases exposure at the lowest level of the stack.
Language Runtimes
EOL runtimes such as Python 2.7 or PHP 7.4 no longer receive security updates. Similarly, reaching Node.js end of life means applications built on these versions inherit every unresolved flaw discovered after support stops.
Libraries and Frameworks
Old libraries and frameworks introduce dependency risk. Even well-maintained applications become vulnerable when a core library is no longer patched.
Databases
EOL databases miss security fixes that protect stored data. This raises the risk of data breaches and compliance violations.
Web Servers and CMS Platforms
EOL web servers and CMS software remain exposed to known exploits. Attackers often target these components first because they are public-facing.
Applications and Middleware
Critical tools like Apache Tomcat, Kafka, and Hadoop also reach EOL. When these stop receiving updates, the data pipelines and services they power become unstable and insecure.
Pro Tip: Always check both the main application and its dependencies, as EOL components can silently introduce vulnerabilities.
Key Support Stages of Software Lifecycle
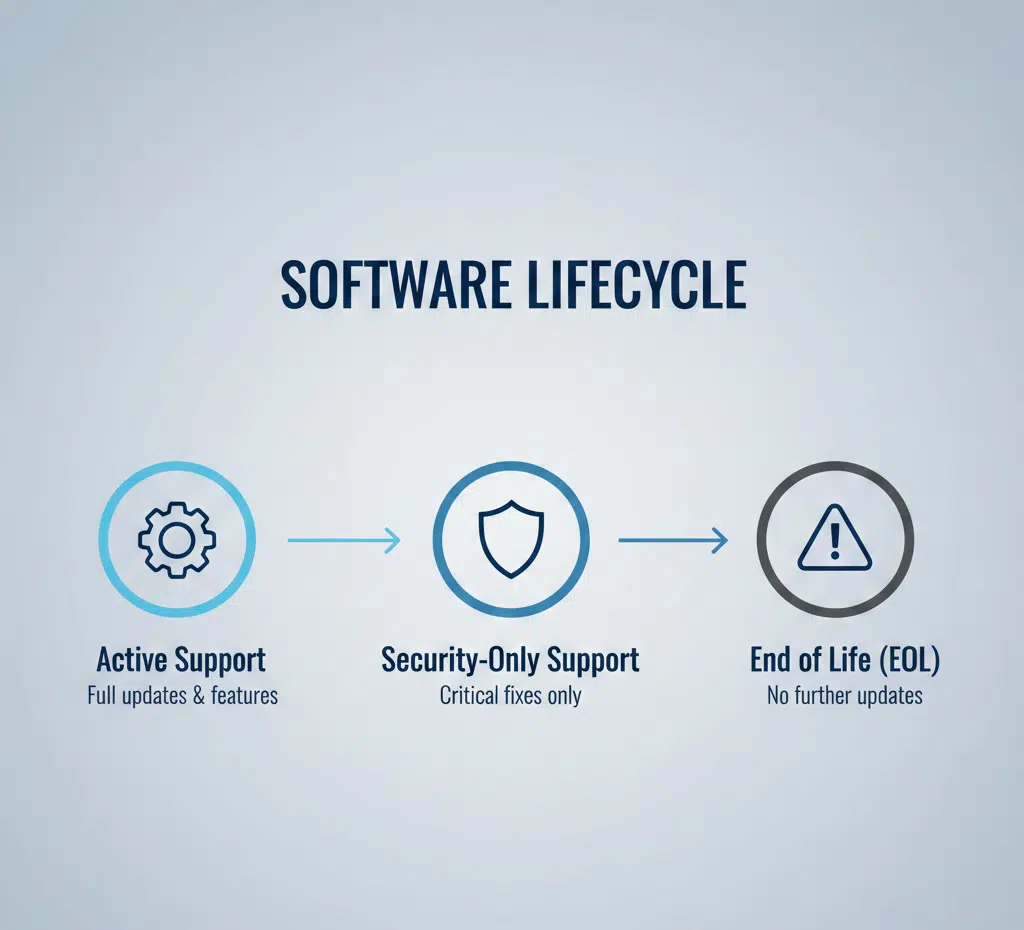
Most software moves through a simple support pattern. What changes is the level of security coverage, not the software itself.
Active support
The vendor provides security patches, bug fixes, and new features. This stage is the safest for production systems.
Maintenance or Security-Only Support
The vendor stops adding new features and improvements. They only provide critical security fixes. Patching happens less frequently during this stage.
End of life
All vendor support ends. No security updates are released, and new vulnerabilities after EOL remain unpatched.
Extended Support
Some vendors offer a paid support after EOL. You pay a fee to get security patches for a certain period of time. This is a temporary fix while you migrate to a new system.
6 Risks of Using EOL Software Without Support
Since EOL software no longer receives security updates from the original vendor, hackers can – and still do – easily target these systems and find vulnerabilities to exploit. Here are the top six risks you need to be aware of.
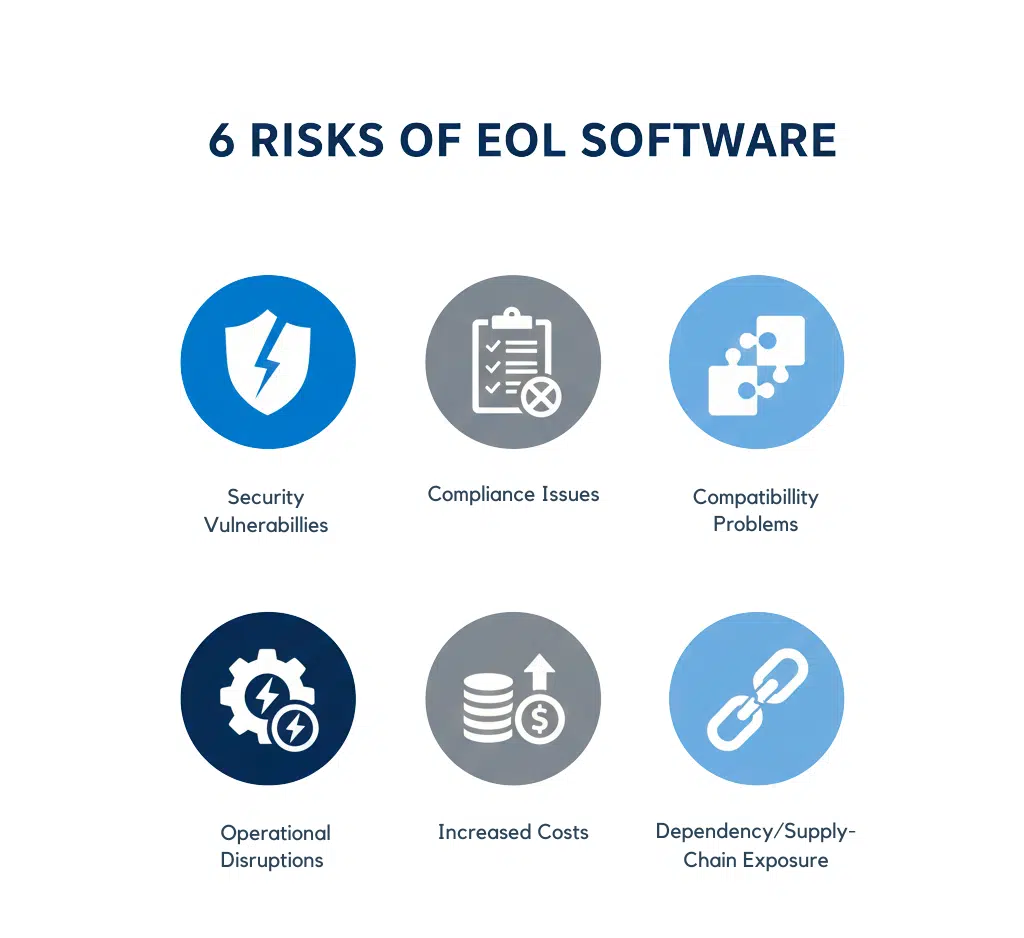
1. Vendors Don’t Patch EOL Software
One of the biggest risks of using EOL software is the lack of security updates. Without these updates, a system is exposed to potential security breaches, leaving sensitive data and information at great risk.
Malicious actors are constantly looking for vulnerabilities in software, and once they find one, they can exploit it to gain access to your system, exfiltrating sensitive data or holding systems for ransom.
2. Compatibility Issues
Another risk of using EOL software is that it may not be compatible with other software or hardware features that you use. This incompatibility leads to system crashes and operational bottlenecks.
For instance, if you are using an end-of-life OS, it may not be compatible with the latest version of a software program you need to use, and this would affect an organization and its employees’ functionality, as well as productivity.
Using EOL software can also limit the organization’s ability to take advantage of new technology and features. Moreover, since new technology and software features are developed regularly, they are also designed to work with the latest software instead of EOL operating systems. If an organization is using end-of-life software, it wouldn’t be able to make the most of new features, setting the company back in terms of productivity and innovation.
3. Increased Cybersecurity Threats
The Cybersecurity and Infrastructure Security Agency (CISA) warns that using end-of-life software increases the chances of data breaches and ransomware attacks, as software vendors will no longer provide security patches and updates to fix newly discovered vulnerabilities.
Since hackers often target EOL software, as they know that many users may continue to use it despite the risks, CISA is encouraging organizations to migrate from whatever end-of-life systems they may still be using.
4. Compliance Challenges
In addition to security risks, CISA also warns that using EOL software can create compliance issues for organizations. There are industry standards and regulations in place for companies that require them to maintain secure and up-to-date software and protect sensitive or prized information from being exposed.
Using software that is beyond its end-of-life date may not meet these requirements, leading to potential violations and legal issues. To mitigate these risks, CISA is advising organizations to develop, implement, and utilize a much more robust software than the EOL ones that they are migrating from.
By doing so, organizations can ensure that they are using the latest, most secure software and can avoid the compliance risks and challenges that come with using EOL software.
5. Increased Costs
Using end-of-life software can increase costs for organizations due to a lack of support from software vendors or when vendors no longer provide security patches, bug fixes, or updates. This leaves organizations vulnerable to security breaches – which can be costly to clean up after.
Moreover, since technical support for software that has reached its end-of-life date is often no longer available either, it can be incredibly challenging to resolve issues. Organizations must often allocate disproportionate resources to maintain aging systems. These hidden costs include hiring specialized IT staff to manage legacy code, increased downtime, and the eventual ’emergency’ migration fees that arise when a system finally fails.
Moreover, EOL software can also have compatibility issues with newer hardware or software, which can increase downtime and lead to revenue loss.
6. Dependency and Supply-Chain Exposure
Most software relies on external libraries and system tools. These are called dependencies. When one of these tools reaches EOL, it affects every app that uses it. Your main app may still have support, but an old library inside it can still let hackers in.
This risk is hard to see. Dependencies sit deep in your software stack. Over time, teams forget which parts are still supported. This creates a “blind spot.” Attackers find these unpatched gaps while you assume your systems are safe.
How to Identify EOL Software
Many businesses run outdated software, not knowing it has already reached the end of life. Usually, the vendor sets the end dates, so it’s essential to check your software’s status.
To find EOL dates, you can use these methods:
Check the vendor’s website: Most vendors post “Product Lifecycle” pages with exact dates.
Use Trackers: Sites like endoflife.date aggregate EOL dates for hundreds of software in one place.
Watch for Alerts: Most modern systems will show a desktop or terminal warning when support is near the end.
Recent Examples of Software That Have Reached End of Life
Software follows a set release cycle. Older versions eventually reach EOL. Here are examples of popular software that hit EOL in the last two years.
RHEL 7 (EOL: June 2024)
Red Hat Enterprise Linux 7 no longer gets regular security updates from the vendor. Servers on RHEL 7 face exposure to new vulnerabilities, increasing risk for the whole stack.
You can read more about the security implications and timelines in our full guide on RHEL 7 EOL.
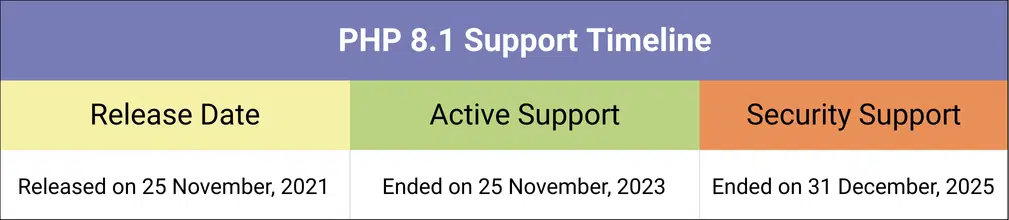
PHP 8.1 (EOL: December 2025)
PHP 8.1 reached EOL at the end of 2025. Applications on this version do not get security fixes for new vulnerabilities. This puts web servers and dependent frameworks at risk of compromise.
PHP powers 72.4% of all websites. While 39.8% of those sites use PHP 8, many stay on older builds. Version 8.1 is used by 22.8% of all sites that run PHP 8, according to W3Techs.
PostgreSQL 13 (EOL: November 2025)
Support for PostgreSQL 13 ended in late 2025. The vendor stopped all patches. Databases on this version face unpatched flaws and compliance challenges.
For information about maintaining PostgreSQL database security on older releases, see our full breakdown.
OpenJDK 11 (EOL: October 2024)
OpenJDK 11 hit EOL in late 2024. Java apps on this version risk runtime flaws. These flaws affect all services linked to the app.
OpenJDK 17, the next LTS version in the Java lifecycle, is also approaching end of life for several distributions, with support windows closing as early as September 2026 depending on the build. Learn what that means for your environment in our guide to OpenJDK 17 EOL.
Oracle Linux 7 (EOL: December 2024)
Oracle Linux 7 reached EOL at the end of 2024. Servers on this OS do not receive vendor updates. This leaves kernel and package-level vulnerabilities unaddressed.
Many of these platforms are supported by TuxCare’s Endless Lifecycle Support, allowing organizations to continue receiving critical security patches even after official vendor support ends.
How to Stay Secure After Software Reaches EOL
Overall, the costs associated with using EOL software can quickly add up – from security risks to operational disruptions. So, organizations should opt for software that is up to date and supported, which will eventually minimize security risks and avoid other unnecessary costs.
However, for a variety of reasons, companies may need to use software beyond its end-of-life date. Fortunately, there are ways to use these systems safely.
Use Extended Support Solutions
After the software vendor stops providing updates, some third-party vendors offer extended support, which includes security fixes for known vulnerabilities, and the landscape of those vendors varies significantly, from OS-focused providers to framework-only tools like HeroDevs.
For a full breakdown, see our comparison of HeroDevs competitors.
This enables you to continue using your existing software versions without worrying about security vulnerabilities.
TuxCare provides Endless Lifecycle Support (ELS) for end-of-life Linux distributions, language runtimes, libraries, and applications, delivering critical security patches after vendor support ends. ELS allows organizations using end-of-life software, like Ubuntu 18.04, .NET 6, or those preparing for .net 8 end of life to keep their systems protected without immediate migration.
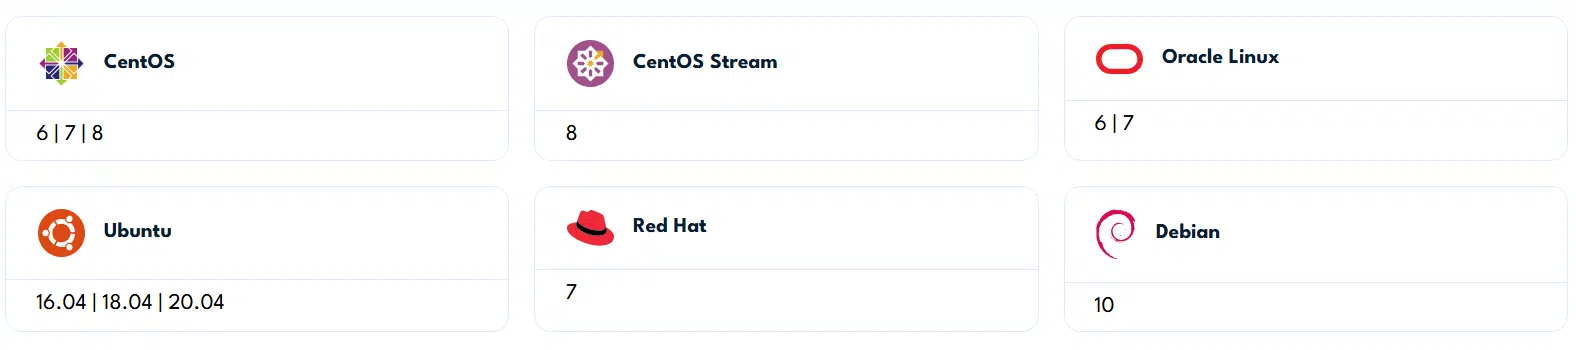
Currently, TuxCare delivers ongoing vulnerability patches for the following EOL Linux distributions:
- CentOS (6, 7, 8)
- CentOS Stream 8
- Oracle Linux (6, 7)
- Ubuntu (16.04, 18.04, 20.04)
- RHEL 7
- Debian 10
You can also check our full analysis of CentOS Stream 9 EOL timelines and risks in our detailed breakdown.
ELS includes security updates for critical packages like the Linux kernel, Apache, PHP, Python, MySQL, glibc, OpenSSL, OpenSSH, and more. Check the CVE tracker page for a complete list of covered packages and addressed vulnerabilities.
TuxCare’s ELS is also available for a wide range of EOL software including Python, PHP, .NET, Spring, PostgreSQL, and many more. You can find all the supported technologies here.
Isolate EOL Systems from the Network
Keeping EOL operating systems in highly restricted network segments is an option. You can limit exposure by using firewalls, VLAN segmentation, or air-gapped environments. However, this adds complexity and workload for network administrators and impacts the systems’ usefulness.
Enforce Strong Access Controls
You can harden EOL Linux systems by:
- Enabling multi-factor authentication (MFA)
- Limiting root user access
- Deploying intrusion detection systems (IDS)
However, these security measures only provide temporary risk reduction – they do not replace security updates or long-term support.
Migrating to New Software Systems
Upgrading to a supported version ensures you receive security updates and support from the original vendor. However, if there is no direct upgrade path, you must either find a replacement or use extended support for continued security.
For example, there is no CentOS 9 to upgrade from CentOS 8, forcing users to switch to CentOS Stream or alternatives like AlmaLinux. Whether upgrading or migrating, the process requires careful planning to minimize downtime and compatibility risks.
Learn how to migrate your CentOS 7 or 8 systems to AlmaLinux with our step-by-step migration guide.
Securing Your EOL Software with Endless Lifecycle Support
While the risks associated with using EOL software past their end-of-life date are quite daunting, there is a solution ready. TuxCare’s Endless Lifecycle Support (ELS) enables organizations to continue using the existing version of software with peace of mind, all while minimizing the risk of security breaches and reducing the typical downtime that comes with using end-of-life software.
Has your organization still not migrated from CentOS 7? TuxCare provides ongoing security patches and updates for EOL open-source software, just like this version of CentOS.
End-of-life Linux doesn’t need to put your organization at risk. Speak to a TuxCare Linux security expert today to learn how your organization can stay secure and compliant beyond end of life.

